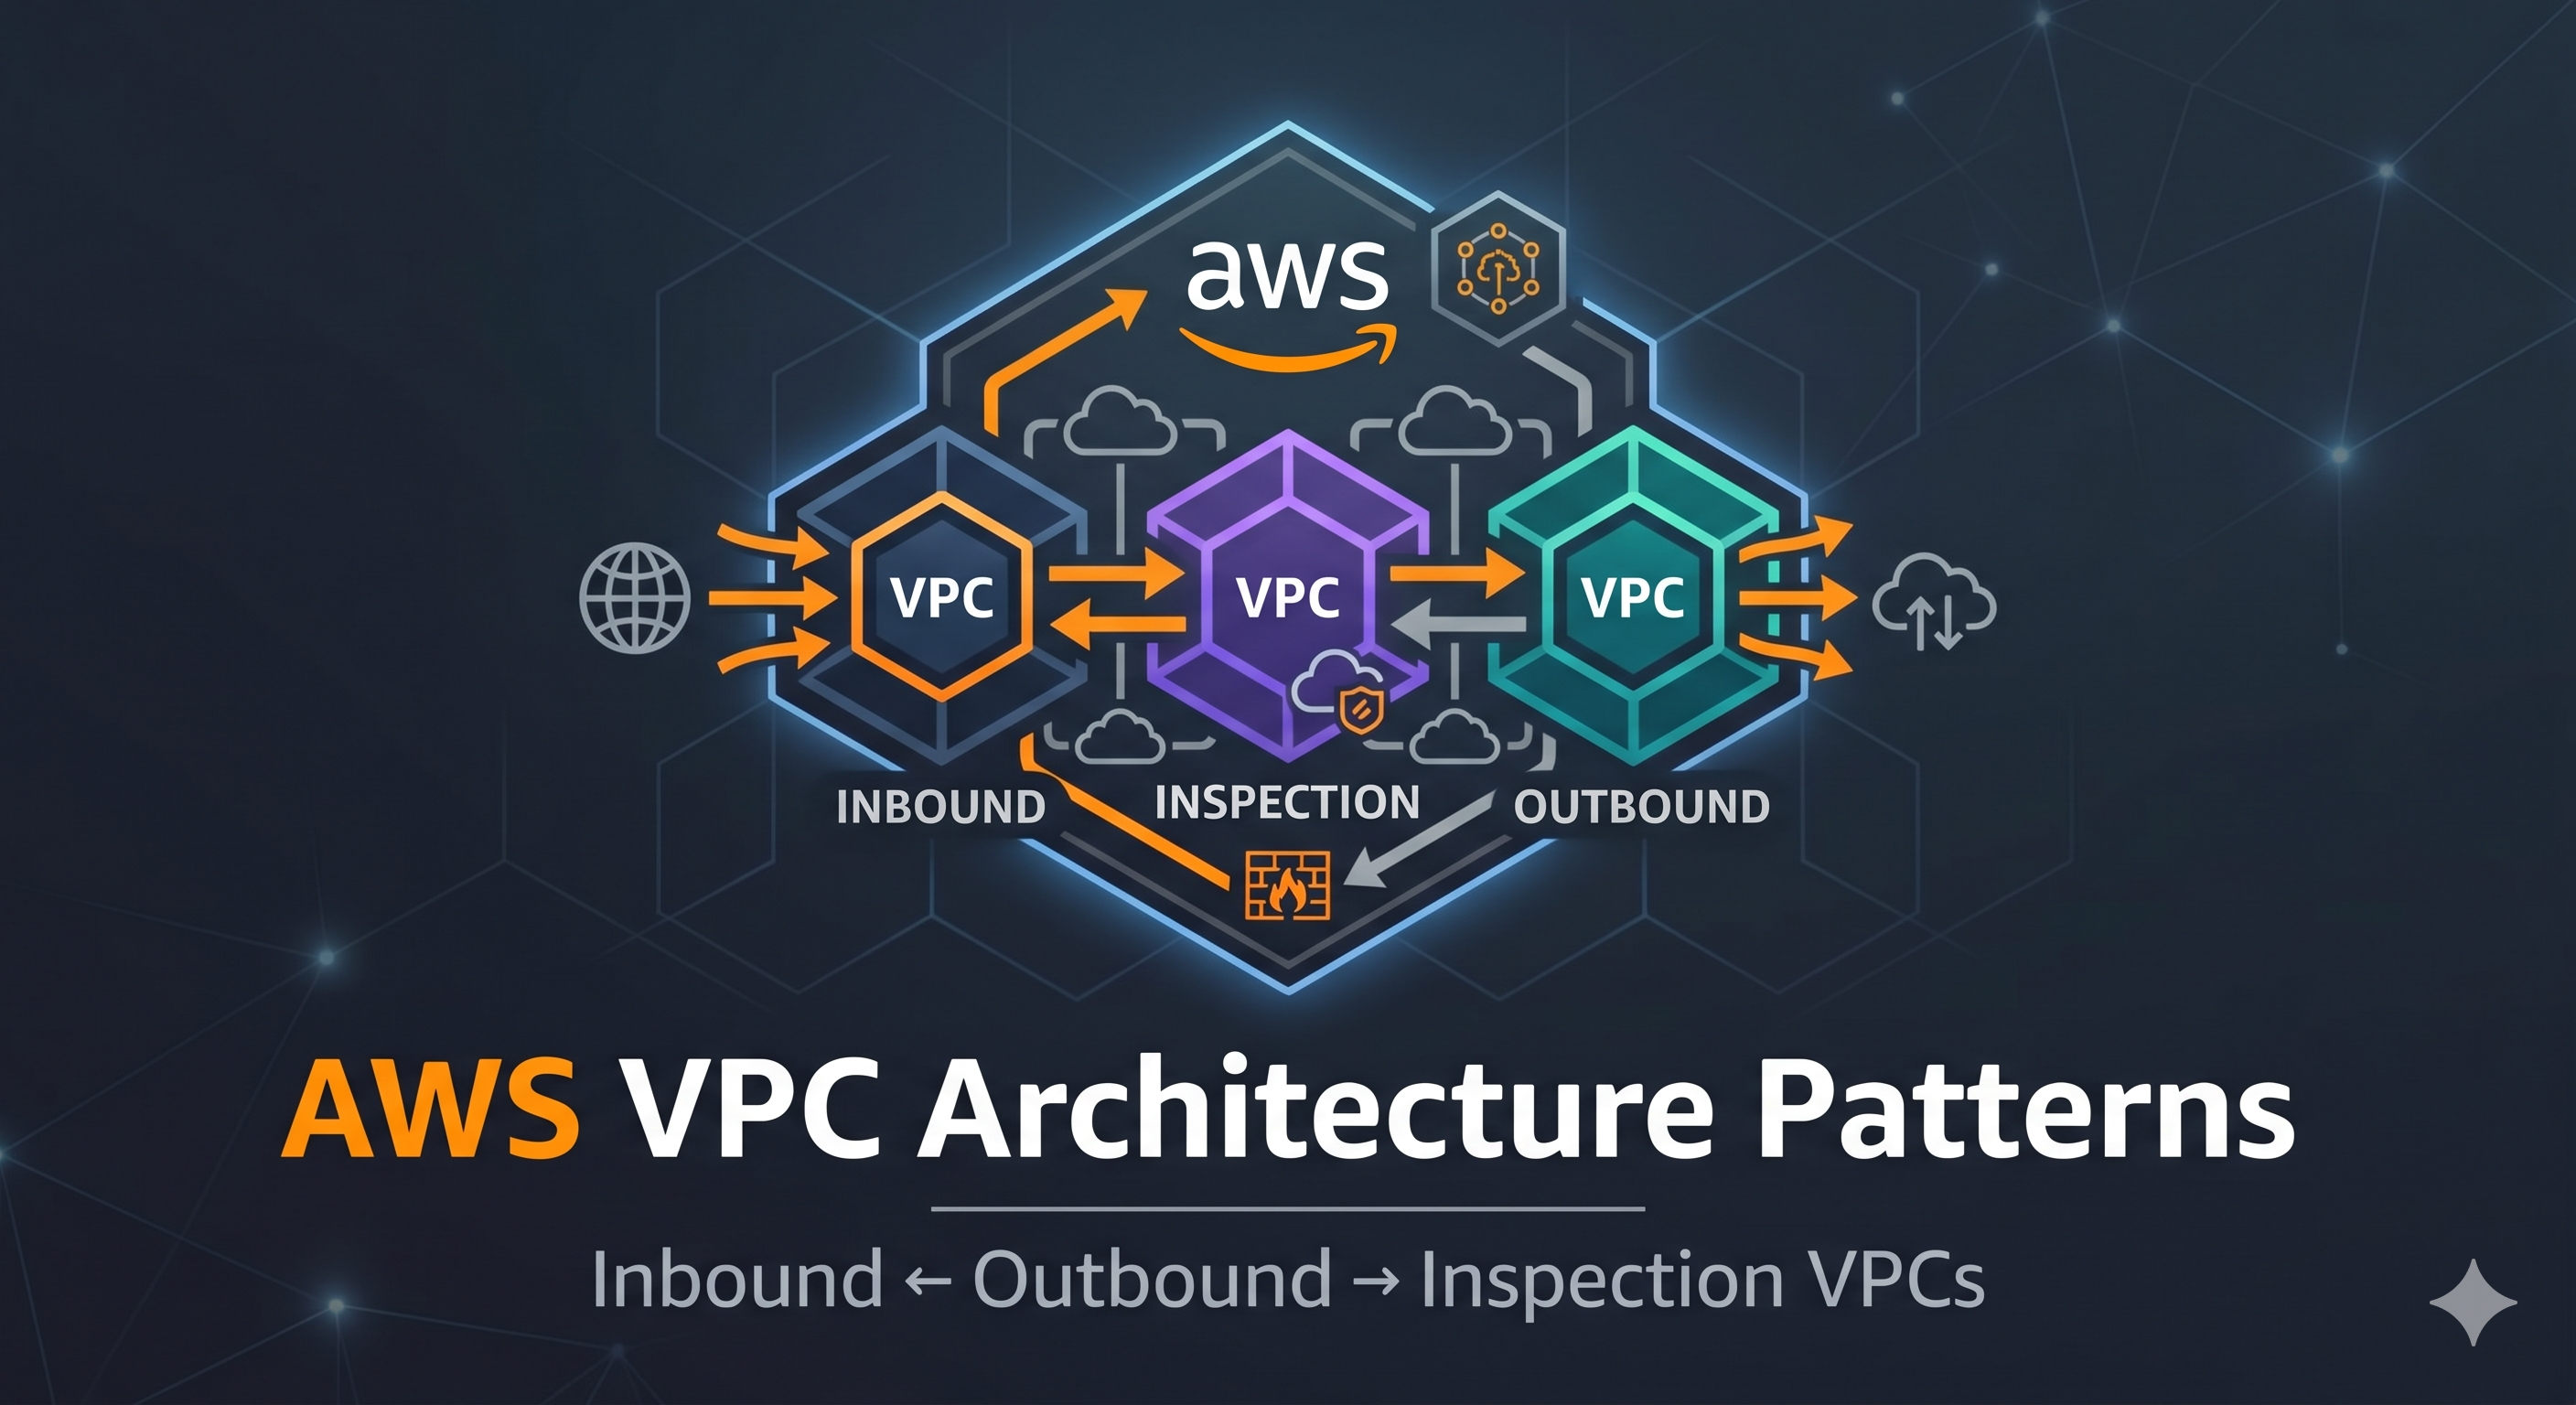
AWS VPC Architecture Patterns - Inbound, Outbound, and Inspection VPCs
A walkthrough of enterprise AWS VPC architecture patterns - inbound, outbound, and inspection VPCs, Transit Gateway hub-and-spoke, and centralized egress and security
A walkthrough of enterprise AWS VPC architecture patterns - inbound, outbound, and inspection VPCs, Transit Gateway hub-and-spoke, and centralized egress and security
In-depth technical walkthrough of TryHackMe Source Code Security covering Git architecture, BitKeeper history, centralized vs distributed VCS, credential hygiene, environment variables, and GitLab secret management.
A deep-dive reference on the core network protocols, how they work, what ports they use, and their security implications. Built for quick lookup during CTFs, pentests, and cloud security work.
A full walkthrough of AWS VPC - subnets, route tables, internet gateways, NAT, security groups, NACLs, flow logs, endpoints, and peering
Technical walkthrough of TryHackMe Intro to Pipeline Automation covering the pipeline stages, version control security, dependency supply chains, build agent contamination, and environment segregation from DEV to PROD.
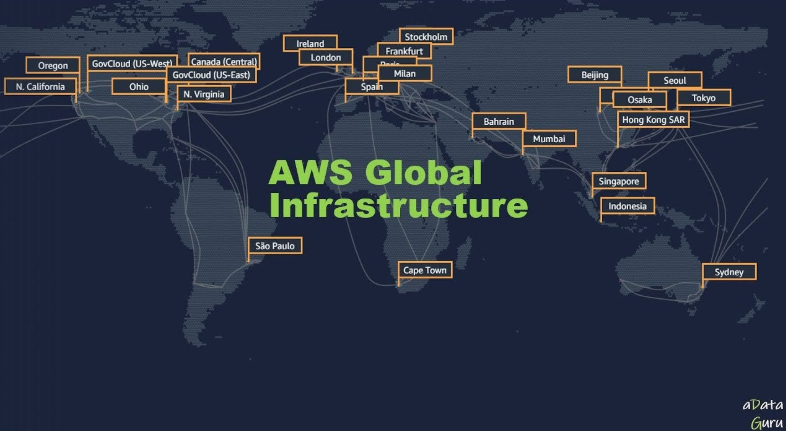
A practical breakdown of how AWS physically organises its global infrastructure - regions, availability zones, edge locations, and why the design matters for resilience and latency
Technical walkthrough of TryHackMe SSDLC covering the integration of security across all SDLC phases, qualitative and quantitative risk analysis, threat modelling frameworks (STRIDE, DREAD, PASTA), security testing automation (SAST, DAST, IAST, RASP), security maturity models (Microsoft SDL, OWASP SAMM, BSIMM), and the Secure Space Lifecycle challenge.
A full walkthrough of AWS Elastic Load Balancing - ALB vs NLB, listeners, target groups, health checks, sticky sessions, and SSL termination
Walkthrough of TryHackMe SDLC covering the 6-8 phases of software development, the CALMS readiness framework, core DevOps velocity and recovery metrics, and the Production of the Droids challenge.
Walkthrough of TryHackMe Introduction to DevSecOps covering the evolution from Waterfall and Agile to DevOps, shift-left security mechanics, cultural pillars, organizational silos, and the Fuel Trouble challenge.